FedRAMP's August Rev5 update: the sponsorless pipeline opens, new Rev5 packages end June 11, 2027, and missed rules bring corrective plans
FedRAMP opened Rev5 Class B and C Program Certification to Lost Sponsor and Ready Conversion providers on August 10, 2026. New Rev5 packages must reach FedRAMP by June 11, 2027, FedRAMP plans corrective action plans for missed deadlines, and revocation only after the grace period.
By FedXchange ·
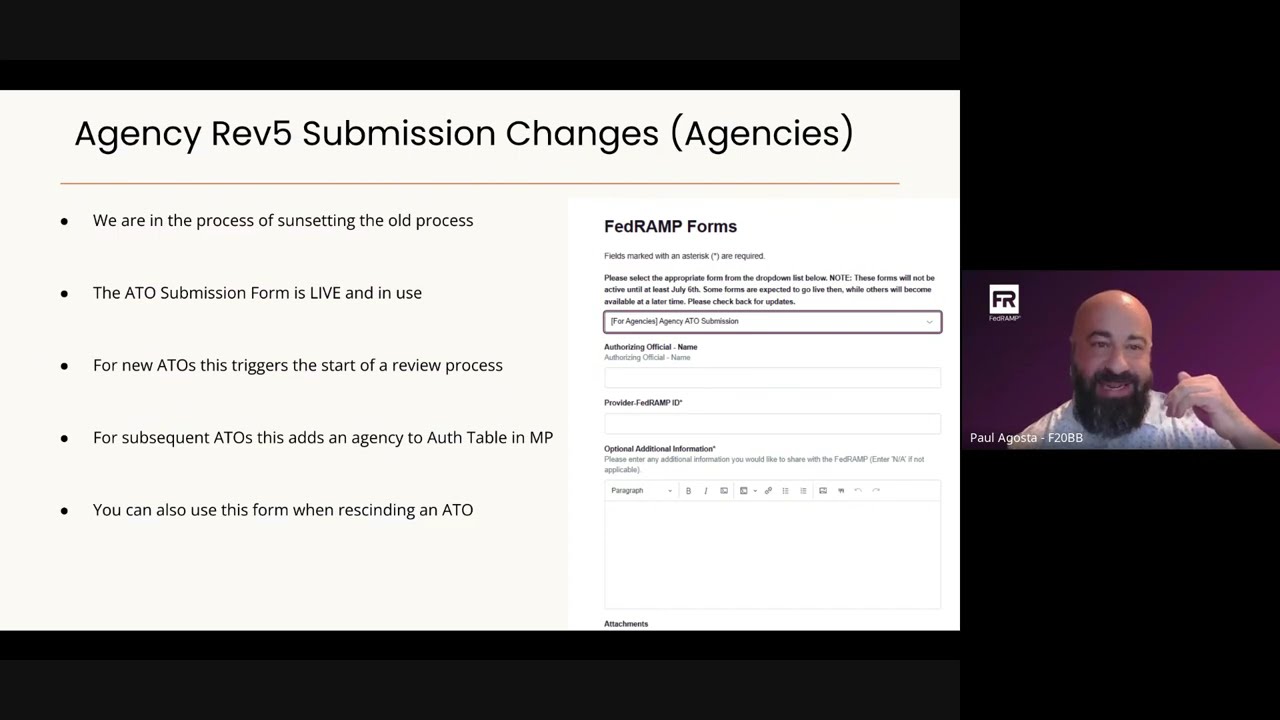 Play the video: FedRAMP Rev5 Community Update
The Federal Risk and Authorization Management Program (FedRAMP) held its monthly Rev5 Community Update on Wednesday, August 5, 2026. Rev5 is the FedRAMP path built on Revision 5 of the National Institute of Standards and Technology (NIST) control catalog. Under the FedRAMP Consolidated Rules for 2026 (CR26), FedRAMP calls its approval a "FedRAMP Certification." This post uses that term.
In short:
- Who it affects: cloud service providers on the Rev5 path, their independent assessors, and the agency staff who sponsor or use their services.
- The sponsorless pipeline opened August 10, 2026. Providers that lost an agency sponsor, or that hold an older FedRAMP Ready result, can apply for a Rev5 Class B or Class C Program Certification. A Program Certification is one FedRAMP grants without an agency sponsor. Class D is not offered on this path.
- June 11, 2027 is the cutoff. On that date, FedRAMP stops accepting applications for new Rev5 Certifications. A FedRAMP leader said a package not listed as FedRAMP In Process by then will not be certified under Rev5.
- Missed rule deadlines: FedRAMP plans to require a corrective action plan when a provider misses a CR26 rule's deadline. It plans to look at revoking certifications after the grace period ends.
- Agencies: send ATO letters through FedRAMP's form, not by email.
Sources: the FedRAMP Rev5 Community Update video (August 5, 2026) and FedRAMP's Choose a Path page.
Read the steps as text
- Check the dates. Between January 2025 and March 2026, the service lost its sponsor while In Process, completed a Security Assessment Report (SAR), completed a Readiness Assessment Report (RAR), or became FedRAMP Ready.
- Submit the right form. Use the Lost Sponsor Form for a lost sponsor or a SAR. Use the Ready Conversion Form for a RAR or FedRAMP Ready. The forms opened August 10, 2026.
- Book a kickoff meeting. The provider books a 30-minute meeting with the Rev5 team through a self-scheduling link.
- Close the gaps. FedRAMP looks at the state of the documents, the routine security upkeep, and the CR26 rules in place. The provider finishes what is missing.
- Send the readiness form. The provider says it is ready and completes the package checklist, now with a list of CR26 rules followed.
- FedRAMP review. FedRAMP's target is 30 calendar days. The clock pauses while FedRAMP waits on the provider.
Does our service qualify for the sponsorless pipeline?
FedRAMP's Choose a Path page sets the test. Between January 2025 and March 2026, the service must have done one of these:
- Been In Process on the FedRAMP Marketplace and then lost its sponsor.
- Completed a full assessment with a Security Assessment Plan and SAR, under an informal agency agreement.
- Completed a FedRAMP Ready assessment with a RAR.
- Achieved FedRAMP Ready on the Marketplace.
The first two use the Lost Sponsor Form. The last two use the Ready Conversion Form. The pipeline came from Notice 0008, the outcome of RFC-0023 on Rev5 Program Certifications.
A FedRAMP leader stressed that the dates decide who qualifies, and that FedRAMP will not bend them. The leader said the team gets two to three emails a day asking about dates outside the window. In the video, the leader asked providers not to send these emails.
Qualifying is not the same as being ready. The standards for a certification have not changed. A FedRAMP Ready result alone is not enough; the provider needs a full package. A provider that qualifies through a Marketplace listing needs no proof of the date. A provider that qualifies through a SAR or RAR date must bring the dated SAR or signed RAR, or bring the assessor who can confirm the date, to the kickoff meeting.
The kickoff meeting is mainly for finding gaps, not for turning people away. The leader asked providers to bring staff who can answer questions about the assessment, continuous monitoring, and the system as it is today. The leader also said that the longer a provider waits to submit, the more CR26 rules it must meet.
Applicants agree to follow all updated Rev5 rules by February 19, 2027. As of November 8, 2026, FedRAMP's page says the pipelines close June 11, 2027.
What does the June 11, 2027 deadline mean for a Rev5 package?
FedRAMP's timeline says that on June 11, 2027, "FedRAMP will no longer accept applications for new FedRAMP Rev5 Certifications." A FedRAMP leader said this covers new packages and uplifts to a higher class, since FedRAMP treats an uplift as a new submission. By that date the package must be complete and the independent assessment done. On the agency path, the agency's authorization to operate (ATO) must already be submitted.
The leader walked through cases from questions sent to FedRAMP:
| Situation | What FedRAMP said |
|---|---|
| Certified, annual assessment due November 2026 | Still do the assessment. Include the rules due by the time FedRAMP receives the results, not the rules due when the assessment started. |
| Initial assessment set for May 14, 2027 | Finishing the assessment, getting an agency ATO, and submitting in 28 days is very unlikely. Consider 20x, FedRAMP's newer path. |
| In Process, waiting on an agency review set for February 2027 | Agency reviews vary. FedRAMP has seen some take two months and some take 16. The provider must work out the timeline with the agency. |
FedRAMP's review target is 30 calendar days, and the leader said reviews were averaging under 30. The clock pauses when FedRAMP sends a package back for fixes.
What happens if we miss a CR26 rule's deadline?
A FedRAMP staff member said FedRAMP plans to put corrective action plans in place for providers that miss a rule's first deadline. It plans to look at revoking certifications once a rule's grace period ends. Some rules will be enforced more strictly. The staff member named Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER), which follow from a Cybersecurity and Infrastructure Security Agency (CISA) binding operational directive. That directive is BOD 26-04. FedRAMP had already moved the VDR and VER dates in Notice 0014 on June 16, 2026: both are mandatory December 7, 2026, and a service can keep its certification under a corrective action plan through March 7, 2027.
The staff member asked providers that expect to slip to tell FedRAMP early, with a proposed plan and dates.
FedRAMP is adding a page to its package checklist that lists each CR26 rule as followed or not. It flags a rule past its first deadline and asks for a plan of action and milestones (POA&M) item. If the rule is past its grace period, it tells the provider not to submit.
Asked whether a provider that misses a "must" statement before the grace date is out of compliance, a FedRAMP staff member said technically yes. FedRAMP will look at what is done, the plan to fix the rest, and other safeguards in place. The staff member said the packages exist to show agencies the risk.
To show that a rule set is in place, read each rule. Some need a formal notice, such as an email to FedRAMP when leaving Connect.gov for the provider's own trust center. A FedRAMP leader advised treating each move to a new rule set as a significant change, so customers know.
What changed for agencies and for forms?
- ATO letters. FedRAMP's form for submitting an ATO letter is live. Agencies use it for a first ATO, a later ATO, an update, or a rescinded ATO. CR26 rule AGU-AGC-NAA on agency use requires agencies to notify FedRAMP when they authorize a service. A FedRAMP leader said forms reach the right staff faster than email.
- Requests beyond FedRAMP. Rule AGU-AGC-NAI says agencies must notify FedRAMP after asking a certified service for more than FedRAMP requires. A FedRAMP staff member said this helps FedRAMP see which old practices, such as POA&Ms, agencies still ask for.
- Provider forms. The provider information form and the Marketplace listing form were combined into one form at help.fedramp.gov. A FedRAMP leader said new submissions and Marketplace updates must now include a machine-readable submission in JSON (JavaScript Object Notation).
- Significant changes. A FedRAMP staff member said FedRAMP accepts its Significant Change Notification (SCN) process now. A provider must still manage what its agency contracts require. Rule SCN-CSO-INF requires a copy of the business or security impact analysis with each notification.
What else did FedRAMP answer?
- Moving from Rev5 to 20x. FedRAMP had not announced a transition date. A FedRAMP staff member said providers should adopt the CR26 rules first. Key Security Indicators (KSIs) belong to 20x. There is no mapping from old KSI names to new ones.
- FIPS 140-2. FedRAMP's frequently asked question on FIPS 140-2 says these modules go historical on September 21, 2026. NIST's FIPS 140-3 transition page gives September 21, 2026 in its overview, and its schedule table lists September 22. A provider can stay on the historical module or move early to an unapproved 140-3 module, and track either as an open vulnerability.
- Losing a sponsor. A certified Rev5 service that loses its only agency sponsor stays certified and keeps up continuous monitoring. It does not become a Program Certification.
- Defense Information Systems Agency (DISA). FedRAMP and DISA do not accept each other's results.
Which requests for comment did FedRAMP preview?
- Offerings By Government. RFC-0032 covers services an agency runs for other agencies. The operating agency needs its own ATO. FedRAMP's list of requests for comment shows comments closed September 8, 2026.
- 20x Phase 4. The video expected a request for comment in late August or early September 2026 for Class D pilots from October to March. It appeared as RFC-0033 and closed October 9, 2026.
- Retiring LI-SaaS. A FedRAMP leader said FedRAMP plans to stop new FedRAMP Tailored for Low-Impact Software-as-a-Service (LI-SaaS) packages, with Rev5 Class B or 20x Class B as the other paths. As of November 8, 2026, that request for comment is not on FedRAMP's list.
Sources
- FedXchange tracker: FedRAMP Rev5 Community Update, August 2026
- YouTube: FedRAMP Rev5 Community Update
- FedRAMP Consolidated Rules for 2026
- FedRAMP: Choose a Path
- FedRAMP: Important Dates for the Consolidated Rules for 2026
- FedRAMP Notice 0008: Initial Outcome from RFC-0023 Rev5 Program Certifications
- FedRAMP RFC-0023: Rev5 Program Certifications
- FedRAMP: Agency Use of FedRAMP Certified Cloud Services
- FedRAMP: Significant Change Notification
- FedRAMP help: guidance on the sunsetting of FIPS 140-2
- NIST: FIPS 140-3 Transition Effort
- CISA BOD 26-04
- Notice 0014: FedRAMP Response to CISA BOD 26-04
- RFC-0032: Offerings By Government and FedRAMP's RFC-0032
- RFC-0033: 20x Phase 4 Development Tracks for 20x Class D
- FedRAMP: Requests for Comment
- FedRAMP Tailored LI-SaaS
Get new posts and federal governance by email
A weekly email on Fridays, an alert on the day the watch finds something new, or both. Free.